
Palo Alto Networks News of the Week – November 1

Here’s all of the Palo Alto Networks news from the past week.

Once in a while, you come across a story that grabs your attention and makes you wonder how it would apply to your own situation. Last year, one such story was the film ‘Her.’ It portrayed an everyday person falling in love with an everyday technology called OS1 and its voice Samantha. The analogy? We meet customers every day who tell us that they’ve fallen in love with our platform. So in honor of our customers, meet PAN-OS…

Unit 42 examines an information stealer campaign that leveraged a VBA macro script and focuses on its progression, from delivery to Command and Control (C2), and its attribution to a malicious actor for context on objectives and motivation.

Because many businesses are aggressively pursuing Internet of Things (IoT) initiatives with the goal of creating revenue-generating opportunities, Isabelle Dumont touches on the importance of protecting critical infrastructure, properly securing all devices that are connected to the Internet, and how best to approach security of IoT.

Check out Rick Howard’s interview with ISMG’s Tom Field on “How to Put Survey Results to Work,” where he talks candidly about his gut reaction to the recent Advanced Persistent Threats Survey results, the latest APT tactics and solutions, and how organizations should approach 2015 security investments.

We’re on the road with VMware and VMUG in the U.S. and Canada to discuss how you can strengthen your data center security without compromising application performance. Find an event near you to learn best practices for implementing advanced security services in a SDDC, to hear customer insights for deploying VMware NSX with micro-segmentation, and to get hands-on experience test-driving an integrated VMware-Palo Alto Networks solution.

PAN-DB is our URL and IP database, designed to fulfill an enterprise’s web security needs. PAN-DB is tightly integrated into PAN-OS, providing you Advanced Persistent Threat (APT) protection with high-performance beyond traditional URL filtering. Here are a few web security tips from Tsugunori Sugawara on how PAN-DB works.


Read about how RWE selected Palo Alto Networks to guard high-stakes financial and energy data from endpoint exploits in this month’s Customer Spotlight.


We’re on the road across North and South America with Citrix and CA for the next few weeks, talking about how enterprises can streamline virtualized data centers, radically simplify network services for delivering critical applications and reduce complexity and cost – all without sacrificing performance and security. Join us at an event near you.


Here are upcoming events around the world that you should know about:

Datacenter Consolidation Seminar Series – Anaheim, CA

  • When: November 4, 2014 11:00 AM – 1:30 PM PST
  • Where: Anaheim, CA

Datacenter Consolidation Seminar Series – Denver, CO

  • When: November 4, 2014 11:00 AM – 2:30 PM MST
  • Where: Denver, CO

Datacenter Consolidation Seminar Series – Edmonton, AB

  • When: November 4, 2014 11:00 AM – 2:30 PM MST
  • Where: Edmonton, AB

Datacenter Consolidation Seminar Series – Seattle, WA

  • When: November 4, 2014 11:00 AM – 1:30 PM PST
  • Where: Seattle, WA

Palo Alto Networks & Westcon Security Seminar [Italian]

  • When: November 4, 2014 10:00 AM – 2:30 PM CET
  • Where: Roma

Datacenter Consolidation Seminar Series – Calgary, AB

  • When: November 5, 2014 11:00 AM – 1:00 PM MST
  • Where: Calgary, AB

Datacenter Consolidation Seminar Series – Dallas, TX

  • When: November 5, 2014 11:00 AM – 1:00 PM CST
  • Where: Dallas, TX

Opplev styrken i Next-Generation Brannmurer [Norwegian]

  • When: November 5, 2014 1:00 PM – 2:00 PM MEZ
  • Where: Online

Palo Alto Networks: Live Demo

  • When: November 5, 2014 9:00 AM – 10:00 AM PST
  • Where: Online Event

Advanced Endpoint Protection with Palo Alto Networks

  • When: November 6, 2014 1:30 PM – 2:30 PM PST
  • Where: Online

Datacenter Consolidation Seminar Series – Cleveland, OH

  • When: November 6, 2014 11:00 AM – 1:00 PM EST
  • Where: Independence, OH

Datacenter Consolidation Seminar Series – Portland, OR

  • When: November 6, 2014 11:00 AM – 1:00 PM PST
  • Where: Portland, OR

Datacenter Consolidation Seminar Series – Scottsdale, AZ

  • When: November 6, 2014 11:00 AM – 1:00 PM MST
  • Where: Scottsdale, AZ

Datacenter Consolidation Seminar Series – Vancouver, BC

  • When: November 6, 2014 11:00 AM – 1:00 PM PST
  • Where: Vancouver, BC

Safe Application Enablement with Palo Alto Networks

  • When: November 6, 2014 10:00 AM – 11:00 AM PST
  • Where: Online

11月7日(金)製品体感セミナー [Japanese]

  • When: November 7, 2014 1:30 PM – 5:00 PM GMT+9:00
  • Where: 千代田区

Datacenter Consolidation Seminar Series – Chicago, IL

  • When: November 11, 2014 11:00 AM – 1:00 PM CST
  • Where: Rosemont, IL

Datacenter Consolidation Seminar Series – Nashville, TN

  • When: November 11, 2014 2:30 PM – 5:00 PM CST
  • Where: Nashville, TN

You Can Have It All

  • When: November 11, 2014 11:30 AM – 1:30 PM CST
  • Where: New Orleans, LA

11月12日(水)製品導入・運用支援トレーニング [Japanese]

  • When: November 12, 2014 1:30 PM – 5:00 PM GMT+9:00
  • Where: 千代田区

Datacenter Consolidation Seminar Series – Salt Lake City, UT

  • When: November 12, 2014 11:00 AM – 1:00 PM MST
  • Where: Salt Lake City, UT

Datacenter Consolidation Seminar Series – Santiago, Chile

  • When: November 12, 2014 12:00 PM – 2:00 PM GMT-4:00
  • Where: Las Condes Región Metropolitana

Datacenter Consolidation Seminar Series – Toronto, ON

  • When: November 12, 2014 11:00 AM – 2:00 PM EST
  • Where: Toronto, ON

Palo Alto Networks: Live Demo

  • When: November 12, 2014 9:00 AM – 10:00 AM PST
  • Where: Online

Datacenter Consolidation Seminar Series – Buenos Aires, Argentina

  • When: November 13, 2014 12:00 PM – 3:00 PM GMT-3:00
  • Where: Buenos Aires

Datacenter Consolidation Seminar Series – Los Angeles, CA

  • When: November 13, 2014 11:00 AM – 2:00 PM PST
  • Where: Los Angeles, CA

Datacenter Consolidation Seminar Series – Montreal, QC

  • When: November 13, 2014 11:00 AM – 2:00 PM EST
  • Where: Montreal, QC

Er du forberedt til å håndtere ukjente trussler i ditt nettverk? [Norwegian]

  • When: November 13, 2014 1:00 PM – 1:30 PM CET
  • Where: Online

11月14日(金)製品実感トレーニング [Japanese]

  • When: November 14, 2014 1:30 PM – 5:00 PM GMT+9:00
  • Where: 千代田区

[Palo Alto Networks Blog]

9 New Features and Topics to Check Out in PAN-OS 6.1

The much anticipated PAN-OS 6.1 is finally here and with it, many new topics to read that describe new features and functionality. Here are some recommendations, hand-picked by the Technical Publications team, to add to your reading list.

New Feature Documentation

Local Signature Generation Support for WF-500 Appliances

The WF-500 appliance can now generate signatures locally, eliminating the need to send any data to the public cloud in order to block malicious content. For more information, seeSignature/URL Generation on a WF-500 Appliance.

Per App VPN for GlobalProtect

Leveraging the GlobalProtect Mobile Security Manager App Store feature introduced in GlobalProtect 6.1, the GlobalProtect app for iOS now supports Per App VPN. With Per App VPN, GlobalProtect can route all managed business apps through your corporate VPN, while allowing personal apps direct access to the Internet. For business apps with Per App VPN enabled, if the business app is unable to connect to the corporate VPN, the app will be unavailable to the user and will not send traffic until the secure connection is established. Users will still have access to their unmanaged apps, giving them the freedom to user their devices for personal use while protecting your critical business traffic. For more information, see Isolate Business Traffic.

Use Case: VM-Series Firewalls as GlobalProtect Gateways in AWS

If your users are more physically distributed than the supporting network infrastructure, GlobalProtect gateways in AWS remove the barriers to providing consistent security for all your users. The VM-Series firewall in AWS melds the security and IT logistics required to consistently and reliably protect devices used by mobile users in regions where you do not have a presence. By deploying the VM-Series firewall in the AWS cloud you can quickly and easily deploy GlobalProtect gateways around the world, and extend the corporate acceptable use policy to protect mobile users from threats and risky applications.  For more information on how to deploy this solution, see Use Case: VM-Series Firewalls as Global Protect Gateways in AWS!

LACP Support

The firewall can now use Link Aggregation Control Protocol (LACP) to manage the interfaces in an aggregate group. Enabling LACP improves device and network availability by providing redundancy within aggregate groups and automating interface failure detection. For more information, see LACP.

Session End Reason Logging Support

Traffic logs now include a session end reason field to help troubleshoot connectivity and application availability issues in firewall traffic. For more information, see Session End Reason Logging.

New Documentation on Existing Features

In addition to new feature documentation, we’ve also expanded the depth of information about the following features.

Virtual Systems

Virtual systems are separate, logical firewall instances within a Palo Alto Networks firewall, which provide segmented administration and scalability of a firewall, along with reduced capital and operational expenses. For more information about benefits, use cases, and configuration of virtual systems, external zones, and shared gateways, see Virtual Systems.

Session Settings and Timeouts

This new topic describes settings and timers for TCP, UDP, and ICMPv6 sessions, in addition to IPv6, NAT64, jumbo frame size, MTU, accelerated aging, and captive portal authentication settings. For more information, see Session Settings and Timeouts.

DHCP

This new topic describes the Dynamic Host Configuration Protocol and how to configure interfaces on the firewall to act as a DHCP server, client, or relay agent. DHCP provides network addresses along with TCP/IP and link-layer configuration parameters to dynamically configured hosts. For more information, see DHCP.

NAT

This new topic describes source and destination Network Address Translation, NAT rule capacities, and the ability to configure Dynamic IP and Port NAT oversubscription. For more information, see NAT.

Want More PAN-OS 6.1 Documentation?

Check out the New Features Guide 6.1 and the PAN-OS 6.1 Release Notes on the Technical Documentation Site, or select the 6.1 facet (under OS Version) on the Document Search page!

Happy reading!

Your friendly Technical Publications team

[Palo Alto Networks Blog]

Examining a VBA-Initiated Infostealer Campaign

While Microsoft documents that leverage malicious, embedded Visual Basic for Applications (VBA) macros are not a new thing, their use has noticeably increased this year, thanks in part to their simplicity and effectiveness.

Some threat actors commonly use this class of malware to drop a second stage payload on victim systems. Even though Microsoft attempts to mitigate this threat by disabling macros by default, the percentage of users who explicitly bypass this protection and enable macros remains high.

Exploiting the human factor, the most effective attacker strategy is the tried and true spear phishing attack, ideally made to look authentic by appearing to originate from a legitimate organization/individual and containing role-relevant or topic-of-interest content to entice its intended target. This post examines an information stealer campaign that leveraged a VBA macro script, focusing on its progression, from delivery to Command and Control (C2), and its attribution to a malicious actor for context on objectives and motivation.

Delivery and Exploitation

The recent campaign started with an email sent to an employee responsible for processing financial statements at a global financial organization (Figure 1). The sender’s email address was spoofed as originating from an energy company. Subsequent analysis would show that this façade was very thin; yet, it is often all that is required to encourage a user to open an attachment or click on a link that then executes malicious code.

Figure 1: Delivery of a phishing message containing malicious DOC file

The above e-mail employs common pressure tactics for phishing messages. Specifically, it touches on two areas of potential concern for a target: financial responsibility and the introduction of a state of uncertainty and confusion. In this case, the role of the target as a processor of financial statements might mean that the target is accustomed to receiving similarly structured legitimate e-mails; accordingly, they may open a malicious attachment without a second thought.

The second factor is much broader and relates to how humans deal with uncertainty. Without specific awareness and training, some users may be inclined to open the attachment, wondering why the e-mail was sent to them. In psychology, this is referred to as the “Need for Closure” personality trap.

The next layer of this attack is found within the malicious DOC file once a victim opens it. With a system properly configured to protect against automatic execution of VBA macros, no malicious code has been run at this point. Figure 2 presents a screenshot of the malicious attachment’s displayed contents.

Figure 2: Displayed contents of malicious DOC file, TTAdvise.doc

This content further compounds the two points of concern for the target, and now presents a convenient option of clicking on “Enable Content” to obtain closure on the matter. Despite a security warning (Figure 3), a number of users still choose to enable respective content, allowing for malicious VBA macros to run on their system.

Figure 3: Often ignored Microsoft security warning against enabling macro content

After enabling macros, none of the promised data is shown to the victim; however, the malicious VBA macro script executes in the background without the user’s knowledge.

VBA Macro Script

The embedded VBA macro script is shown in Figure 4.

Figure 4: Embedded VBA macro script

This script operates as a downloader, pulling a second stage payload from the following URL (Note: at the time of this post, the referenced domain was no longer active):

hxxp://icqap.com/oludouble.exe

Installation and Persistence

Static analysis of the “oludouble.exe” binary is summarized in Figure 5.

Figure 5: Static analysis of downloaded second stage malware, oludouble.exe

Once executed, “oludouble.exe” drops two executables (Windows XP paths furnished):

  • C:\Documents and Settings\Administrator\Desktop\exchangepre.exe
  • C:\Documents and Settings\Administrator\Application Data\Windows Update.exe

Both binaries are exact copies (Figure 6).

Figure 6: Files dropped from second stage malware, oludouble.exe

The second stage malware also copies itself to the following directory (Windows XP) and deletes its original file:

C:\Documents and Settings\Administrator\Application Data\Temp.exe

Persistence (enabling the malware to reload after reboot and restart) is achieved through addition of the following registry key, set to the path for the “Windows Update.exe” binary (Figure 7):

HKCU\Software\Microsoft\Windows\CurrentVersion\Run\Windows Update

Figure 7: Windows registry modification for persistence

Malware Capabilities

API Calls extracted from “Windows Update.exe” (b6275be58a539ea9548d02ab6229c768) hints at associated capabilities (Figure 8).

Figure 8: API calls found in “Windows Update.exe” binary

Based on these API calls, the malware appears to support enumeration of a variety of system information. Additionally, the use of “GetAsyncKeyState”, which obtains key press status, could be indicative of keylogging capabilities.

Further investigation and research revealed that this malware leverages the Predator Pain keylogger, a favorite tool of this threat actor. Overall, this malware functions as an information stealer (Infostealer), including capture and exfiltration of the following types of information:

  • Website credentials
  • Financial information
  • Chat session contents
  • Email contents

Command and Control (C2)

Once installed, this malware determines its Internet-facing IP address and then establishes a connection with the following domains:

  • whatismyipaddress.com
  • http://www.myip.ru
  • mail[.]rivardxteriaspte.co[.]uk
  • ftp[.]rivardxteriaspte.co[.]uk

The first two domains are legitimate public IP verification services. The latter two are C2 servers run by the malicious actor, which use SMTP and FTP communications, respectively.

Attribution

E-mail headers are a valuable source of intelligence when investigating these types of attacks (Figure 9).

Figure 9: E-mail headers for phishing message

In this example, when the victim opened the phishing message, it appeared to originate from a legitimate organization. However, closer inspection revealed that the sender address was spoofed through the ‘X-Env-Sender’ header. In an attempt to slide past cursory examination, the malicious actor used an open mail relay, server[.]edm.sg. Another important e-mail header field for this message is ‘Reply-To’, which contains a valid e-mail for this malicious actor:

cimaskozy(at)yahoo.com

Setting the ‘Reply-To’ email header field to a valid address is another common threat actor tactic. It supports elicitation activities by that actor should a target respond to the message (i.e., further social engineering). Yet, this technique should also present a red flag to a user, as the initial façade of the originating e-mail address is removed at that point.

Research on the above email address reveals that this actor has been active in the cybercrime underground since at least 2010. Specifically, this actor goes by the handle “Skozzy” and is a known carder, seller of compromised credit card information, and facilitator of related services. Accordingly, we categorize “Skozzy” as primarily a cybercrime actor motivated by financial gain, although roles across nation state, cybercrime, hacktivist and ankle-biter/script kiddies are not mutually exclusive and – in fact – continue to become fuzzier over time.

Figure 10 is a screenshot of a YouTube post by “Skozzy”  (skozzy11) from 2010.

Figure 10: YouTube post from “Skozzy”, 2010

Figure 11 is a screenshot from a Pastebin post, also from 2010.

Figure 11: Pastebin post from “Skozzy”, 2010

“Skozzy” is also active on HackForums[.]net and has shared thoughts and experiences related to keylogging tools like Limitless Logger and Predator Pain (Figure 12). Of particular note, the infostealer/keylogger tools that “Skozzy” prefers are able to steal much more than what has been observed so far for this actor.

Figure 12: Posts on HackForums[.]net regarding keyloggers

“Skozzy” also shares that Predator Pain is a preferred tool, as it offers great support (Figure 13).

Figure 13: “Skozzy” prefers the Predator Pain keylogger

Deeper analysis and correlation across domains and samples that we believe related to this threat actor will be covered in subsequent blog content.

Conclusion

This case epitomizes how easy it has become these days to steal sensitive information from victims who fall prey to such campaigns. Associated tools can be bought online for less than $100, which often also includes support packages that rival those of mainstream commercial software.

Stolen information can be used for more than standard credit card fraud. The crossover between malicious actor objectives may include opportunistic aspects of cyber espionage, extortion, identity theft, intellectual capital theft, and much more. It is also important to note that none of the major anti-virus (AV) vendors detected this threat at the time it was delivered. The natural gap between creation of these threats and a corresponding signature for their detection by traditional AV remains a sweet spot for successful malicious campaigns. Therefore, it is increasingly important to properly architect and deploy network and endpoint protections to ensure thorough and effective defense of computing and information assets.

The Palo Alto Networks Enterprise Security Platform is a prime example of technology meant to address and minimize the risk associated with emerging threats. Learn more about the platform here.

[Palo Alto Networks Blog]
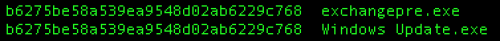
Web Security Tips: How PAN-DB Works

PAN-DB is our URL and IP database, designed to fulfill an enterprise’s web security needs. PAN-DB is tightly integrated into PAN-OS, providing you Advanced Persistent Threat (APT) protection with high-performance beyond traditional URL filtering.

Traditional URL filtering is intended to control unwanted web surfing such as non-business or illegal sites, but it usually doesn’t cover up to the minute malicious web sites such as newly discovered malware site, exploit site or command and control sites. Let me explain how PAN-DB works for you.

How PAN-DB maximizes your URL lookup performance


Figure1. PAN-DB classification and cache system


PAN-DB Core: The PAN-DB Core, located in the Palo Alto Networks threat intelligence cloud, has a full URL and IP database to cover web security needs.

Seed database: When the PAN-DB is enabled on your firewalls, a subset of the full URL database is downloaded from the Palo Alto Networks threat intelligence cloud to firewalls based on the selected geographic region. Each region contains a subset of the URL database that includes URLs most accessed for the given region. This regional subset of the URL database allows the firewalls to store a much smaller URL database, in order to greatly improve URL lookup performance. You can download a seed database by region to the each firewall from our Panorama centralized management system as well.

Figure 2. Seed database by regions

Management plane cache: The seed database is placed into the management plane (MP) cache to provide quick URL lookups. The MP cache will pull more URLs and categories from the PAN-DB core as users access sites that are not currently in the MP cache. If the URL requested by a user is “unknown” to Palo Alto Networks, the URL will be examined, categorized, and implemented as appropriate.

Dataplane cache: A dataplane cache (DP) contains the most frequently accessed sites for quicker URL lookups.


Malicious URL database delivered from WildFire

Millions of URLs and IPs are classified in a variety of ways. In addition to the “Multi-language classification engine” and the “URL change request from users,” PAN-DB receives malicious URL and IP information from WildFire. Examples of malicious URL and IP database are shown below.

  • Malware Download URL and IP address: Prevent from downloading malware.
  • C&C URL and IP address: Disable malware communications.

The malicious URLs are generated as WildFire identifies unknown malware, zero-day exploits and APTs by executing them in a virtual sandbox environment.


PAN-DB will block malicious URL with low latency

PAN-DB has a superior mechanism to lookup URL faster, and then you will get URL category information without sacrificing the throughput.

The malicious URLs are generated as WildFire identifies unknown malware, zero-day exploits, and Advanced Persistent Threats (APTs) and executes them in a virtual sandbox environment. The ongoing malicious URL updates to PAN-DB allows you to block malware downloads and disable malware command and control communications.

By utilizing malicious URL database, you can block variety of malicious web access and communication without compromising web access performance.

To learn more about web security, please visit our resource page, Control Web Activity with URL Filtering.

[Palo Alto Networks Blog]

You’ve Never Seen Love This Deep For An Enterprise Security Platform

Once in a while, you come across a story that grabs your attention and makes you wonder how it would apply to your own situation. Last year, one such story was the film ‘Her.’ It portrayed an everyday person falling in love with an everyday technology called OS1 and its voice, Samantha.

The analogy? We meet customers every day who tell us that they’ve fallen in love with our platform. So in honor of our customers, meet PAN-OS…

[Palo Alto Networks Blog]

English
Exit mobile version