Rejoice! Eight New Books Inducted into the Cybersecurity Canon

I am very excited today to announce the 2016 inductees into the Cybersecurity Canon: our hall of fame for cybersecurity books.

2016 March Madness Winner & Cybersecurity Canon Inductee

2016 Inductees selected by the Cybersecurity Canon Committee

The goal of the Cybersecurity Canon Project is to identify a list of must-read books for all cybersecurity practitioners — be they from industry, government or academia — where the content is timeless, genuinely represents an aspect of the community that is true and precise, reflects the highest quality and, if not read, will leave a hole in the cybersecurity professional’s education that will make the practitioner incomplete.

The Cybersecurity Canon Project is not simply a list of books you should read. Indeed, no book makes it onto the candidate list unless a security practitioner makes the case in a book review that we publish on the website, proving the case that this book should be read by all members of the cybersecurity community. Then, a committee of 10 security professionals decides which books make it into the Canon each year. Anybody can submit a book review for consideration. If the committee thinks you made the case, then we add the book to the candidate list.

The Cybersecurity Canon Project has been going on for three years now. The first year, 2014, we had approximately 20 books in the candidate list and selected one to be inducted into the Canon: “We are Anonymous” by Parmy Olson. The second year, 2015, we had approximately 30 books in the candidate list and selected four (See the 2015 list below). This year, we had 45 books in the candidate list and selected eight. We added a twist to the selection process this year by opening up the voting to the Internet in a March Madness type competition. After six rounds of voting, “Zero Day” by Mark Russinovich emerged as the clear and popular winner.

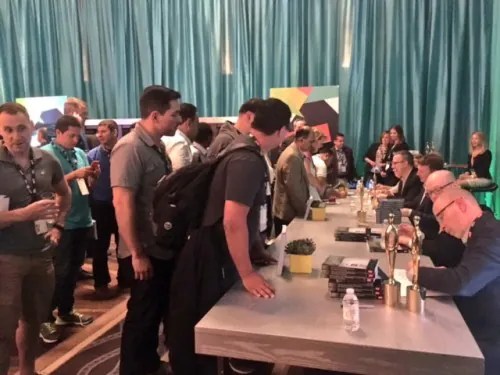
At the awards ceremony, some of the authors received their awards on stage, signed their books for the Ignite 2016 crowd, and shared details about their books in video interviews with members of the Cybersecurity Canon Committee (Stay tuned for videos from the interviews):

  • Dawn M. Cappelli
  • Richard Clarke
  • Marc Goodman
  • Jack Freund
  • Jack Jones
  • Andrew P. Moore
  • Kevin Poulsen
  • Randall F. Trzeciak
  • Liis Vihul

Winners From Previous Years

2015 Inductees selected by the Cybersecurity Canon Committee

  • “Countdown to Zero Day” by Kim Zetter
  • “The Cuckoo’s Egg” by Clifford Stoll
  • “Spam Nation” by Brian Krebs
  • “Winning as a CISO” by Rich Baich

2014 Inductees selected by the Cybersecurity Canon Committee

  • “We are Anonymous” by Parmy Olson

Get Involved

The Cybersecurity Canon Project is a worthy educational endeavor. If you know someone who is trying to learn about what it means to be a cybersecurity professional, consider pointing him or her to our list of books for professional development. If you have a book that guided you in your career, please consider writing a book review for it so that we might get it on the candidate list. Finally, the 2017 Cybersecurity Canon season begins in June. We have a couple of open slots left for the committee. If you are as passionate about cybersecurity books as we are, please reach out to the Cybersecurity Canon committee and tell them you want to volunteer.

[Palo Alto Networks Research Center]

Ignite 2016 Day 1: The Future of Breach Prevention Starts Here

Welcome back to The Cosmopolitan in Las Vegas, where the biggest, boldest, best installment yet of Ignite Conference is already in full swing. Over the next few days, watch this space and follow along on Twitter (@Ignite_Conf and #IgniteConf16) for all the action. For starters, here’s a look at opening day:

Read on for news, photos and updates from the first day of Ignite 2016 and what’s to come on Day 2 and Day 3.

Welcome Back

Ignite 2016 kicked off Sunday with pre-conference Ultimate Test Drives and hands-on workshops designed for security practitioners boning up on the Palo Alto Networks Next-Generation Security Platform. Heading into Monday, we tackled the big questions around how to create an intelligence-led security program, how to create and maintain a disruptive endpoint protection system, how to address IT-OT integration and regulatory compliance in the utilities sector, and many more topics that will continue to drive the cybersecurity conversation this year.

Finally, we convened for a hearty opening reception – and inducted no fewer than eight new books into the Cybersecurity Canon, our hall-of-fame for cybersecurity literature. (Read all about the Cybersecurity Canon and this year’s inductees.)

Today’s Announcements

Coming Up Tomorrow

  • Join us in the general session for some very special guests, including Anthony Zuiker, creator of TV’s CSI franchise, actor and former White House official Kal Penn, and Mark McLaughlin, Lee Klarich and Nir Zuk from Palo Alto Networks
  • The first of two Cyber Range exercises, sponsored by The Wall Street Journal, kicks off at 12:30pm PT. Follow along with all the action using the #IgniteRanger hashtag!
  • Check out more of our tracks and breakout sessions and get psyched for our Tuesday evening event

Stuff For You

Getting Social at Ignite!

See below for some top snaps from the opening day of Ignite 2016 as well as social chatter. You can check out a full gallery of Ignite 2016 photos on our Facebook page – check back for daily updates!

[Palo Alto Networks Research Center]

NextWave Program Evolution, Redefining Next-Generation Security Provider Engagement

It is a great honor to share that Palo Alto Networks recently conducted a global partner satisfaction survey where we achieved a Partner Net Promoter Score of 58 (a score of 50 or higher is considered excellent). To all the partners reading this, thank you! This achievement underscores the strong ties we’ve built with you; the game-changing differentiation of our Next-Generation Security Platform; and, our steadfast commitment to continue evolving our NextWave partner program.

It inspires us to keep redefining how we engage with and enable you to become next-generation security innovators – experts equipped to help mutual customers around the globe prevent successful cyber breaches.

It goes without saying that the cyberthreat landscape is constantly evolving. Today, many different vendors are clamoring about how their pseudo “platforms” – often legacy technologies cobbled together – are the best way for customers to protect themselves against the latest threats. In all of this noise, analysis of some of our most successful partners’ practices indicates that the best way for you to help your customers sift through what’s real and what’s not is through side-by-side technical comparisons.

Our partners who have the expertise to assist in the technical evaluations by becoming next-generation security innovators create deeper relationships with their customers and are more profitable.

With the newest updates to our NextWave Channel Partner Program, we are committed to helping enable this, fostering your success not just by enabling technical differentiation and specializations, but also by enhancing your profitability opportunities, simplifying the way we interact with and support you, and helping you build sustainable, breach prevention-focused security practices. Below are highlights of note in each of these areas.

New differentiation and specializations so you can scale and strengthen your expertise in our technology and become next-generation security innovators:

  • Pre-sales training added to our enablement framework
  • Comprehensive set of pre-sales, sales and post-sales individual accreditations and certifications
  • Nine pre-sales specializations with different levels and expertise by role
  • Roles: foundation, associate and professional
  • Expertise: cybersecurity, platform, endpoint, mobile, data center, platform, cybersecurity and data center.
  • TRAPS advanced endpoint specialization
  • Partners who achieve this will be granted the highest deal registration protection (up to 25 percent) for one year.

New profitability opportunities to achieve higher deal closure rates and reduce cost of doing business include:

  • Improved Diamond and Platform partner margins that reward partners who exceed quarterly growth targets
  • Predictable NFR discounts based on NextWave level
  • Real-time reporting on the utilization of NFR equipment, NFR return-on-investment and proof-of-concept activities

 New loyalty features make it easier to invest in and grow with Palo Alto Networks:

  • Simplified partner framework with new Silver-level requirements
  • Global availability of the highest NextWave Diamond-level partner status
  • An upgraded deal registration system
  • Updated Partner Learning Center
  • New renewals platform

We are pleased to bring these updates to the program and are dedicated to continue helping drive the development of our next-generation security partners and innovators around the globe!

For more information about the updates to the program, please go to our Partner Portal, NextWave Channel Partner Program page where you can find requirement details, overview presentation and partner webcast replay.

[Palo Alto Networks Research Center]

Palo Alto Networks and PwC: Enabling Prevention-focused Cybersecurity

Earlier today at Ignite 2016, our annual user conference, we announced that we are joining forces with PwC’s Cybersecurity Practice to help customers establish security architectures, organizational structures and computing processes optimized to prevent cyber breaches.

Together, we are designing a next-generation security framework to guide customers through establishing a breach prevention-oriented security architecture. This framework incorporates the latest advances in security technology and addresses the modern threat landscape.

To learn more about our partnership, visit Palo Alto Networks & PwC page to read the press release, download an executive overview, and register for a webinar featuring the security framework.

[Palo Alto Networks Research Center]

‘Creating Audit Programs’ White Paper Introduces Template Redesign

With the release of its white paper Information Systems Auditing Tools and Techniques:  Creating Audit Programs, ISACA describes the basic steps to create an audit program. This white paper is part of a series created to deliver practical guidance on how to perform an audit engagement—from planning to reporting and closing—that is consistent with ISACA Auditing Standards (ITAF) as well as those issued by the Public Company Accounting Oversight Board (PCAOB), the Institute of Internal Auditors (IIA), and the American Institute of Certified Public Accountants (AICPA).

Information systems (IS) audits help enterprises ensure effective, efficient, secure and reliable operation of information technology. Audits can also help confirm compliance with numerous legal and administrative regulations, and help management determine if the business is functioning well and meeting challenges. Most importantly, audits assure stakeholders of the organization’s financial, operational and ethical well-being. All of these outcomes are supported by IS audits, especially the information and related technology and systems that most businesses and public institutions rely upon for a competitive advantage.

An important component of the audit plan is the audit program. Audit programs are commonly used to document the specific procedures and steps of testing and verifying control effectiveness. The audit program’s quality has significant impact on the consistency and quality of the audit results, so it is imperative that IS auditors understand how to develop comprehensive audit programs.

The many benefits of an effective audit depend on proper and thorough planning of the audit engagement. To make this happen, the auditor and the area being audited must understand and accept the scope and objective of the audit. Once the purpose is defined, the next step is to create an audit plan that captures the agreed scope, objectives and procedures required to get the relevant, reliable and sufficient evidence to draw and support audit conclusions and opinions.

To demonstrate the process described in the white paper, ISACA has released a sample audit and assurance program developed using a five-step process to gather the necessary information to define the audit subject, objective, scope and audit methodology. The sample audit program for a virtual private network can be customized to create a specific audit and assurance program tailored to your unique needs.

The documents are intended for IT audit professionals who are either new to the profession preparing to the Certified Information Systems Auditor (CISA) or simply want to brush up on their skills.

To learn more see the white paper here.

Eva Sweet, Technical Research Manager, ISACA

[ISACA Now Blog]

English
Exit mobile version